The Continuous Trust Platform
Enterprise-grade trust infrastructure for regulated enterprises across complex markets.
Trusted by Tier 1 banks, financial institutions and regulated platforms across multiple jurisdictions.
Recognised in the Gartner® Magic Quadrant™ for Identity Verification
Built for Multi-Market Complexity.
Identity, regulatory and fraud complexity across jurisdictions.
Regulatory Adaptability
Adapt to evolving KYC, data residency and regulatory requirements across jurisdictions.
Identity Depth
Verify diverse documents, languages and identity ecosystems across markets.
Fraud Resilience
Combine identity, biometric, device and behavioural signals across the customer lifecycle.
Enterprise Deployment
Deploy across markets through configurable journeys, flexible architecture and enterprise integrations.
Industries
One trust layer, configured to your regulator and risk profile.
Tiered KYC, biometric verification, and continuous monitoring, configured to your regulatory requirements.
Meet account-opening regulations across jurisdictions with configurable journeys per product line, audit-grade evidence for every decision, and configurable deployment and residency options.
- ✓Tiered KYC per account class & risk segment
- ✓KYC renewal & re-verification automation
- ✓Regional & private deployment options
The IDWise Trust Platform. One platform across the customer trust lifecycle.
Identity verification, eKYC, fraud intelligence and orchestration in one configurable platform.
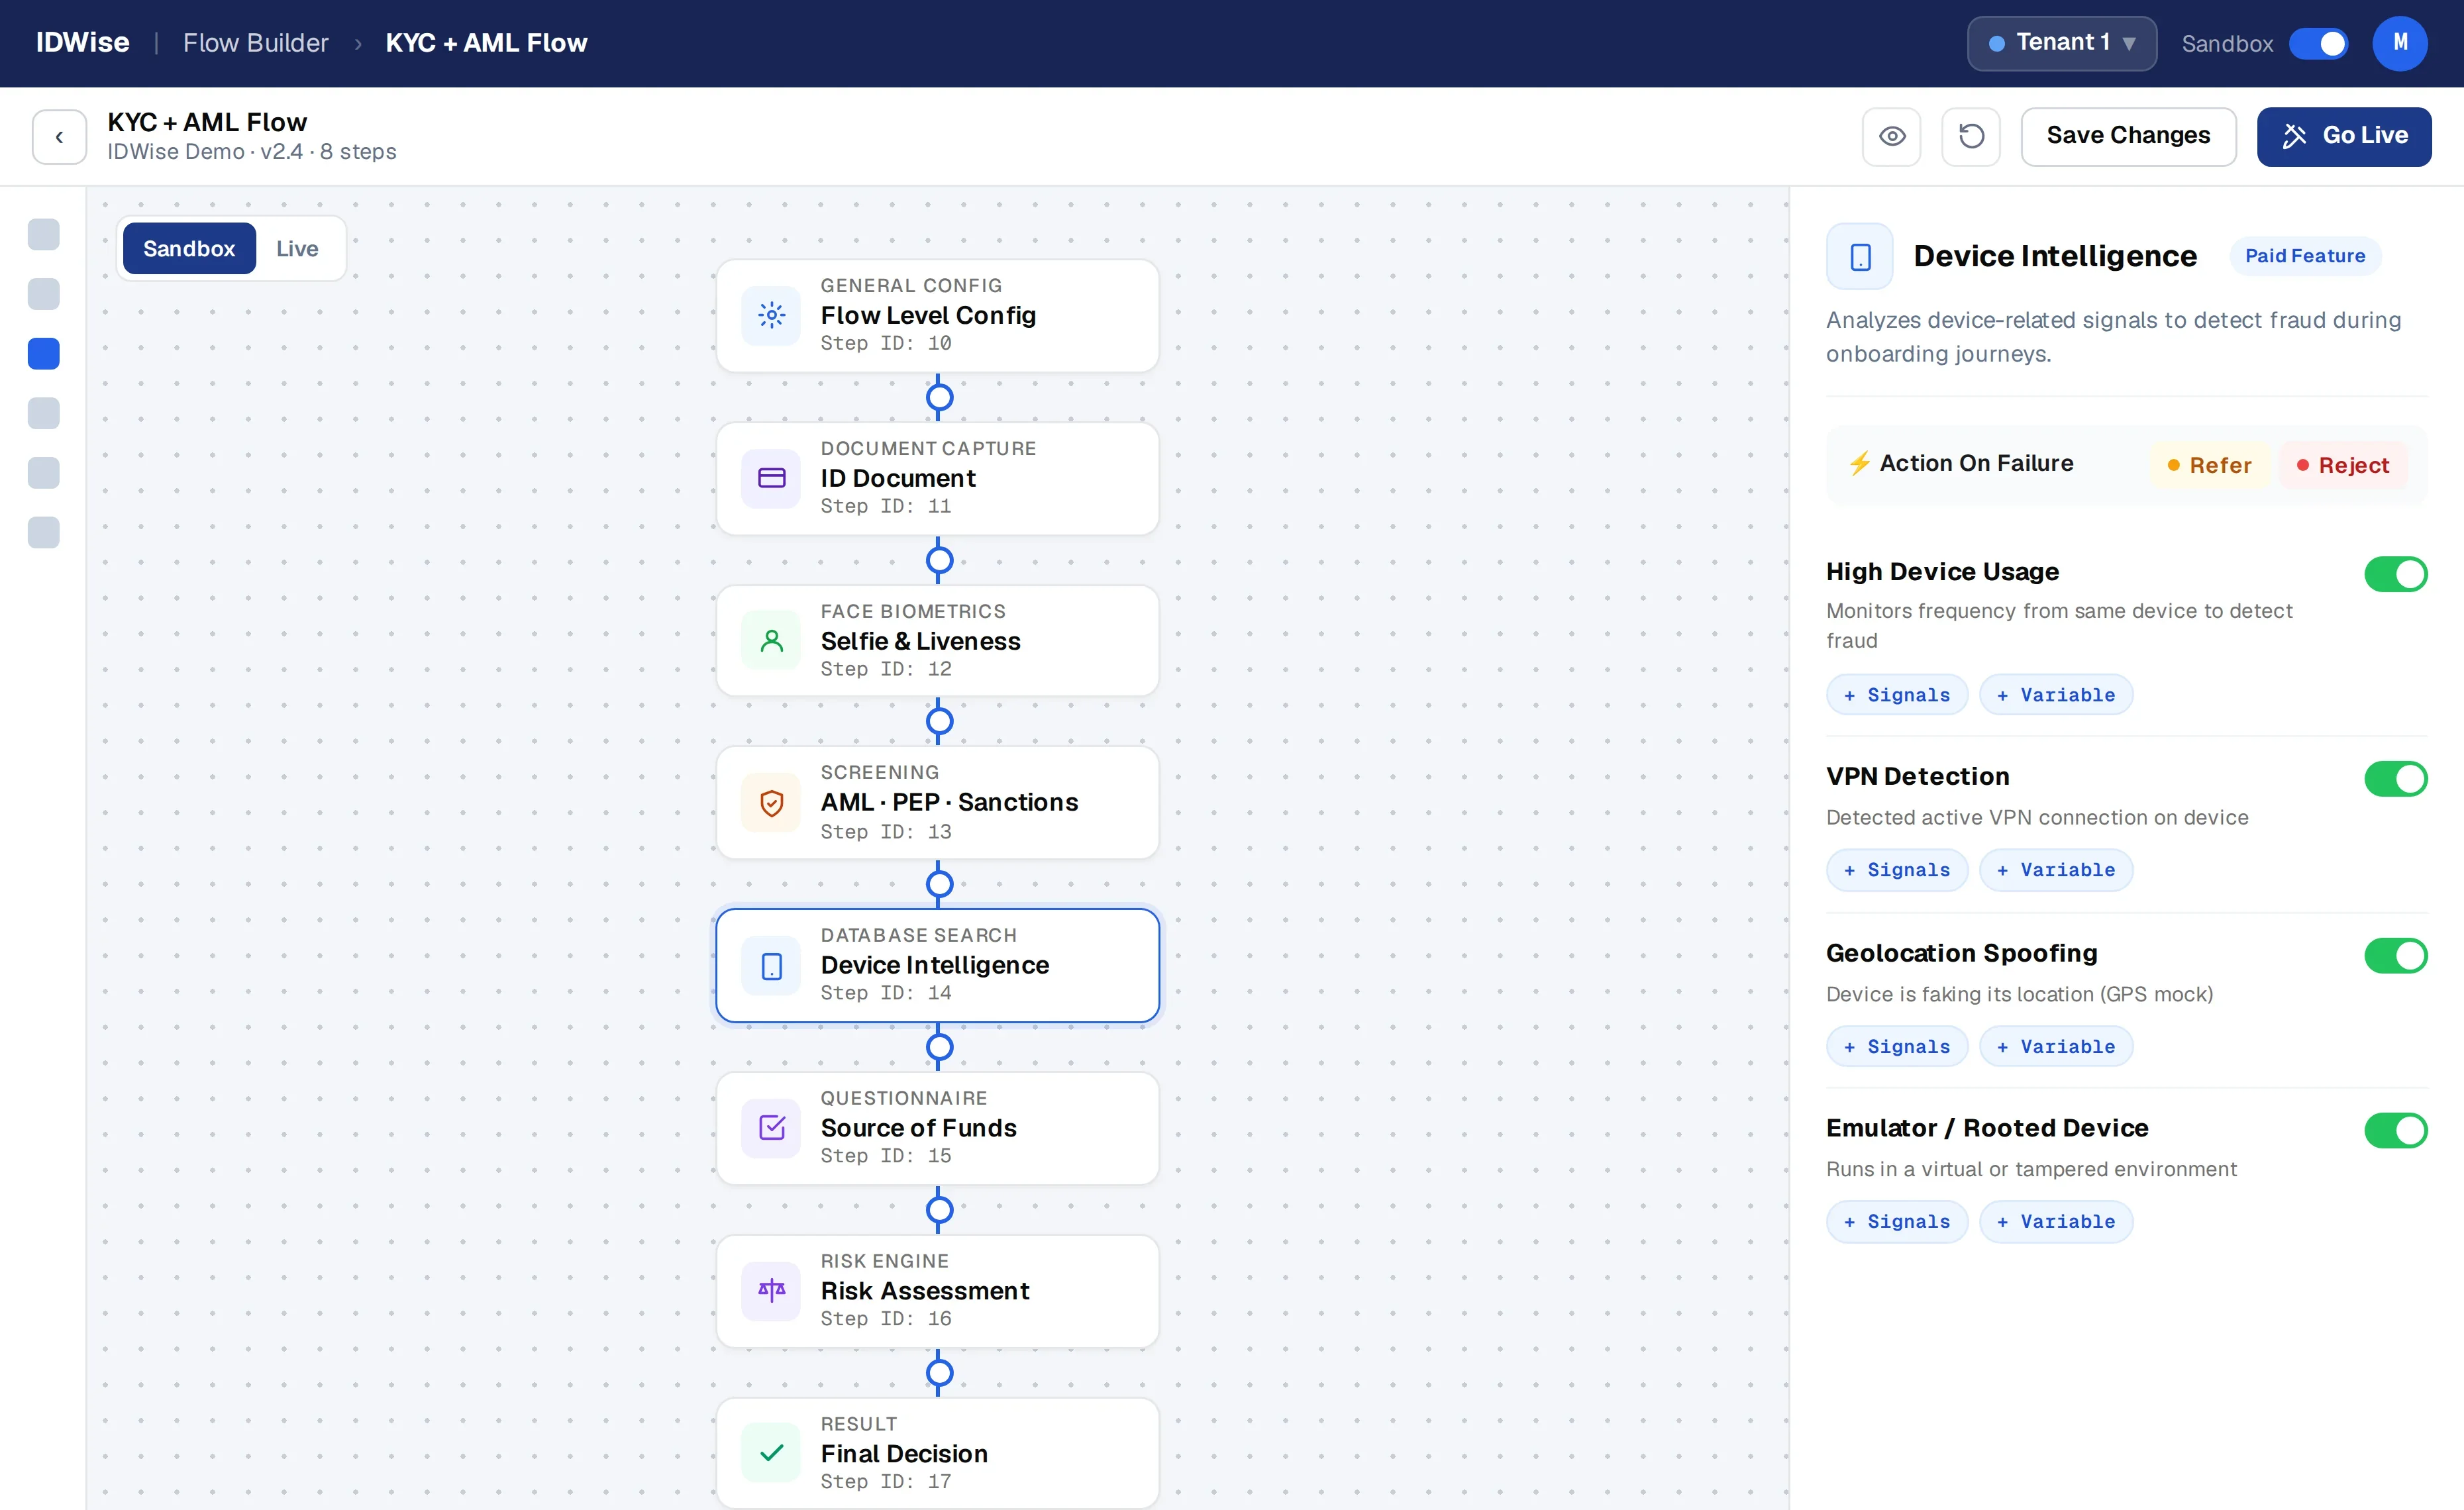
Ship policy changes without an engineering release cycle.
Flow Builder lets compliance and product teams configure journeys, launch new document types, and manage regional variants, without engineering releases. Manage journey configurations centrally across supported channels and SDKs.
Enterprise-Grade Identity, Compliance & Fraud
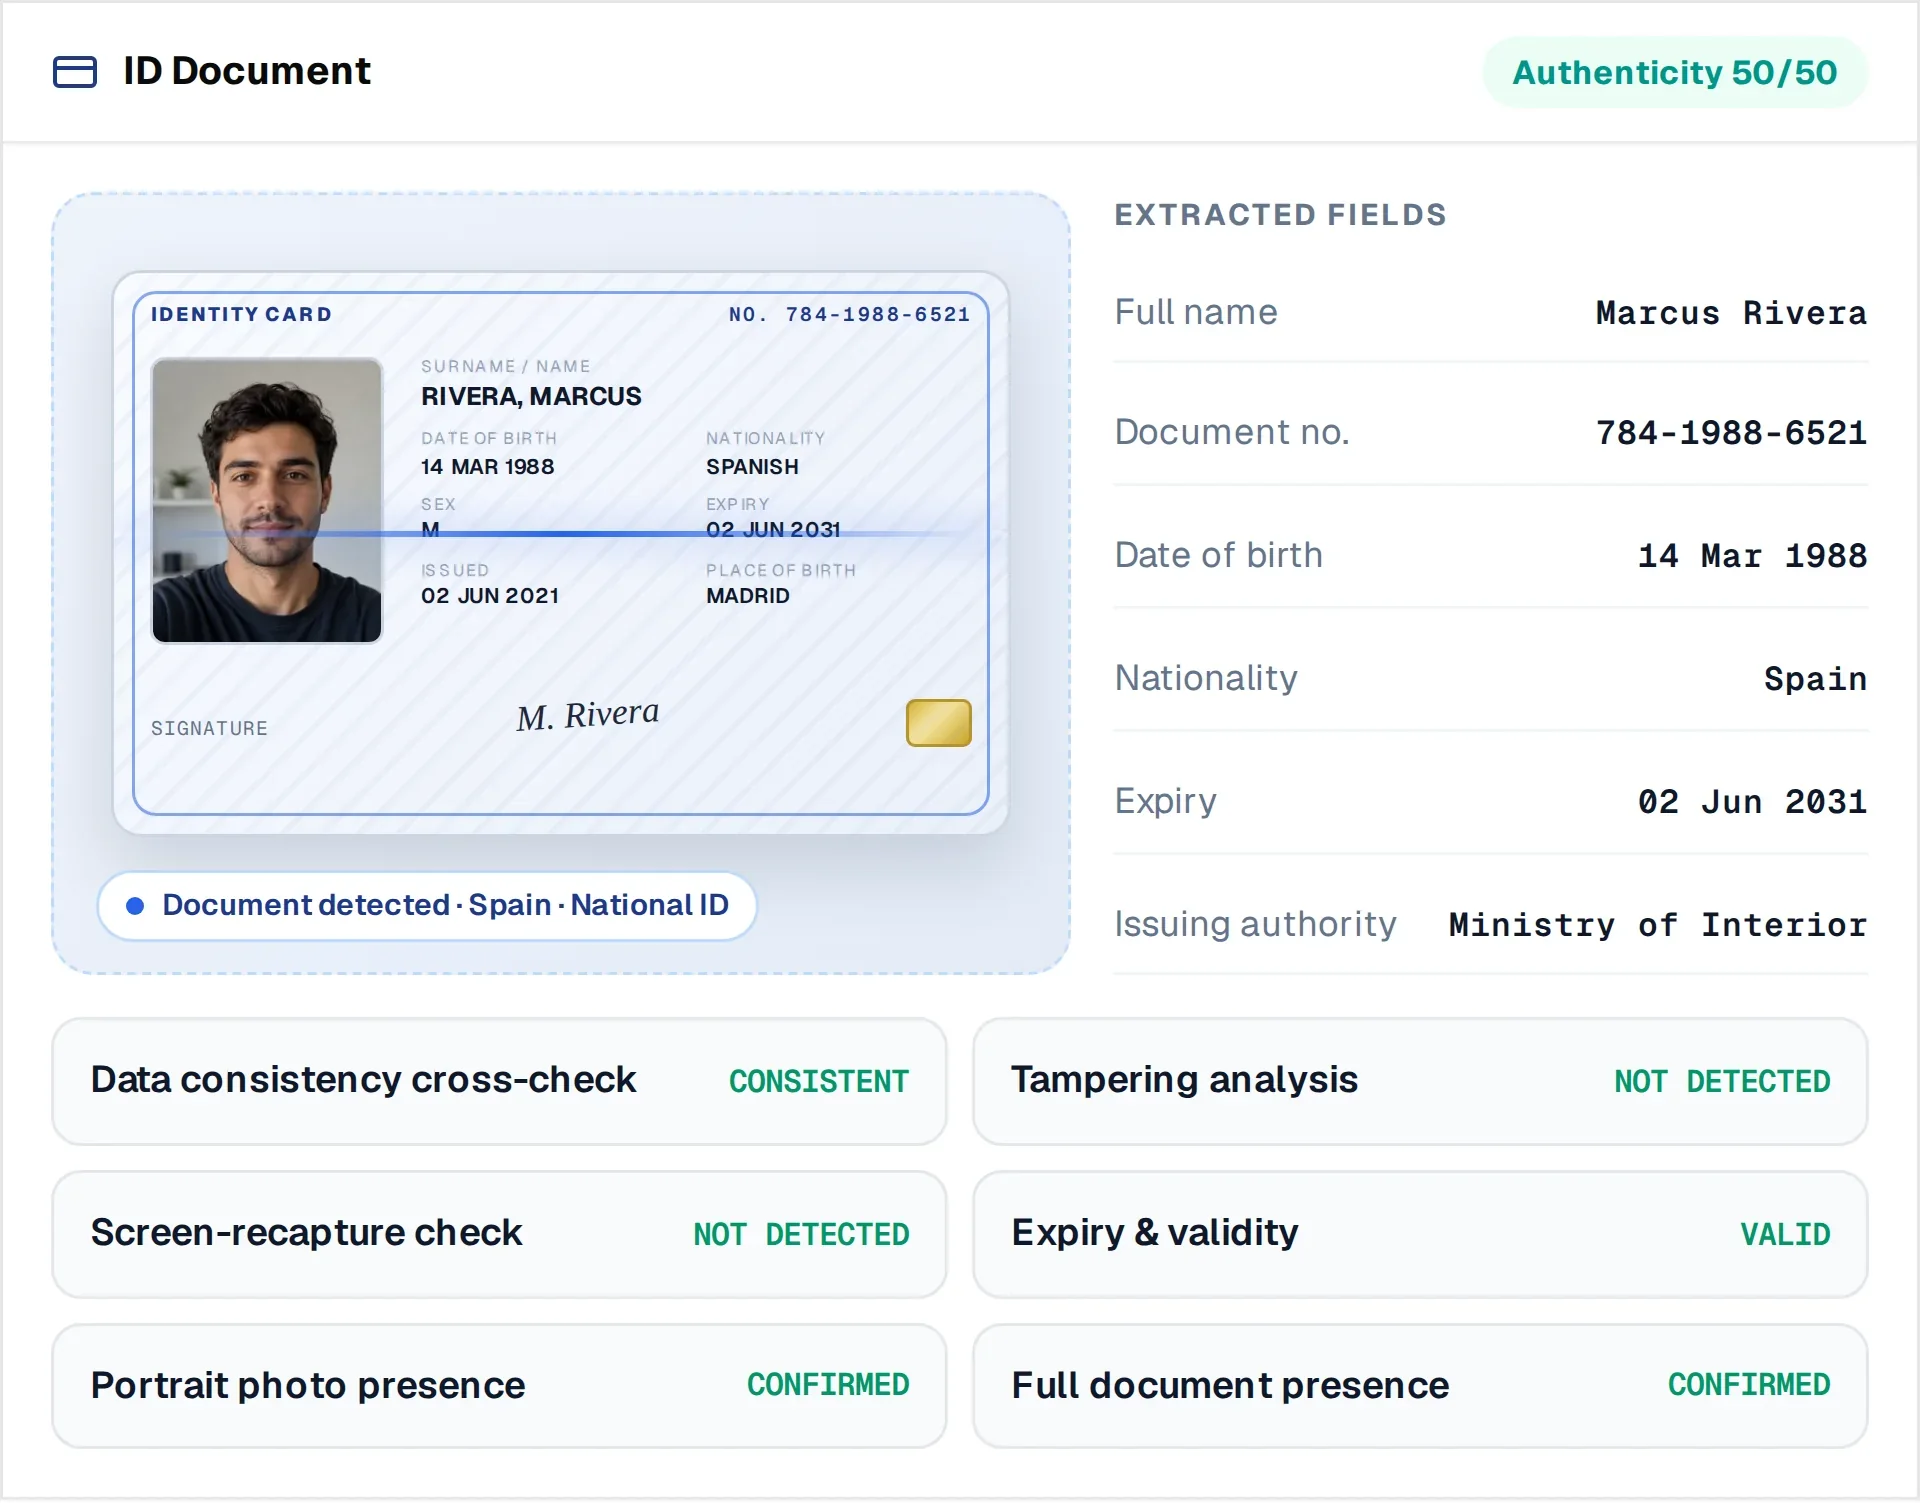
Identity document verification across markets, scripts and formats.
OCR, authenticity, and tampering controls engineered for document diversity, including non-Latin IDs, non-standard formats, and regional conventions a generic engine was never trained on.
- ✓Passports, national IDs & driving licenses across 200+ countries & territories
- ✓50+ security checks per document submission
- ✓MRZ, barcode, and field cross-validation
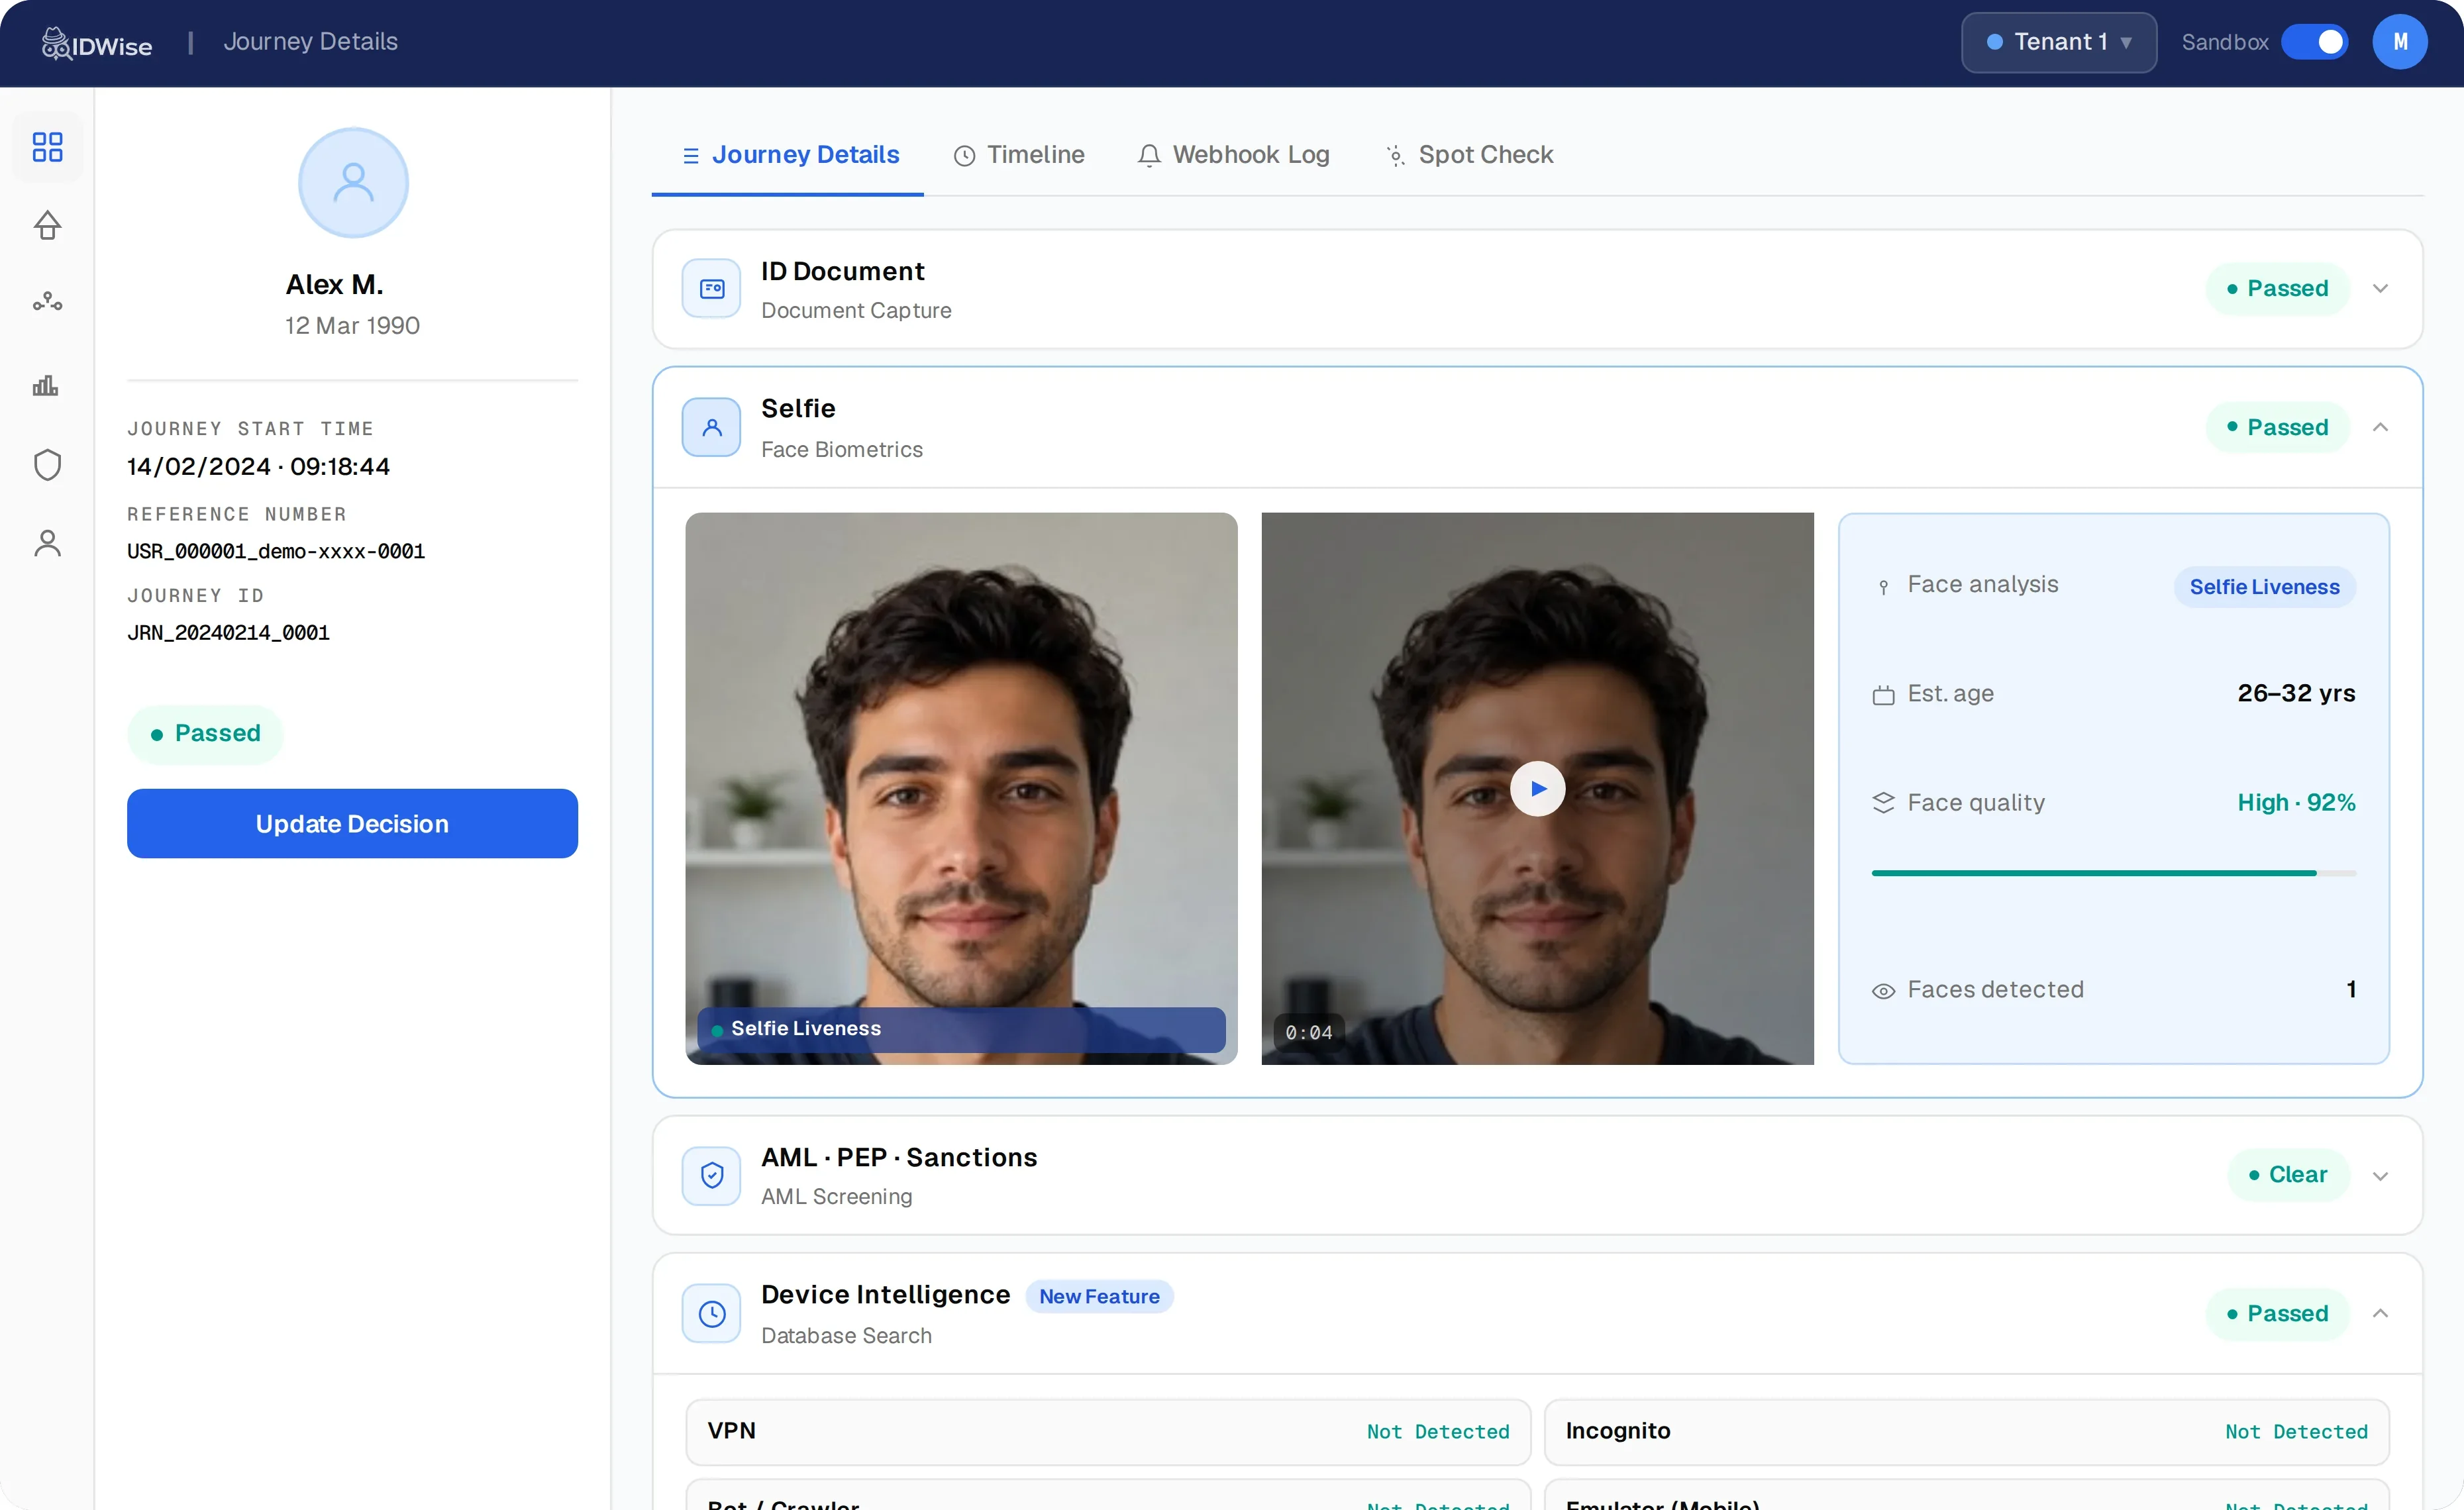
Liveness evaluated where it counts: NIST.
Publicly benchmarked face matching with passive liveness, engineered for biometric diversity across the populations you actually onboard, defended against deepfakes, presentation attacks, and virtual-camera injection.
- ✓Independently benchmarked face matching
- ✓NIST-evaluated passive liveness, no awkward gestures required
- ✓Deepfake & injection-attack defence
- ✓Tuned for low-spec devices
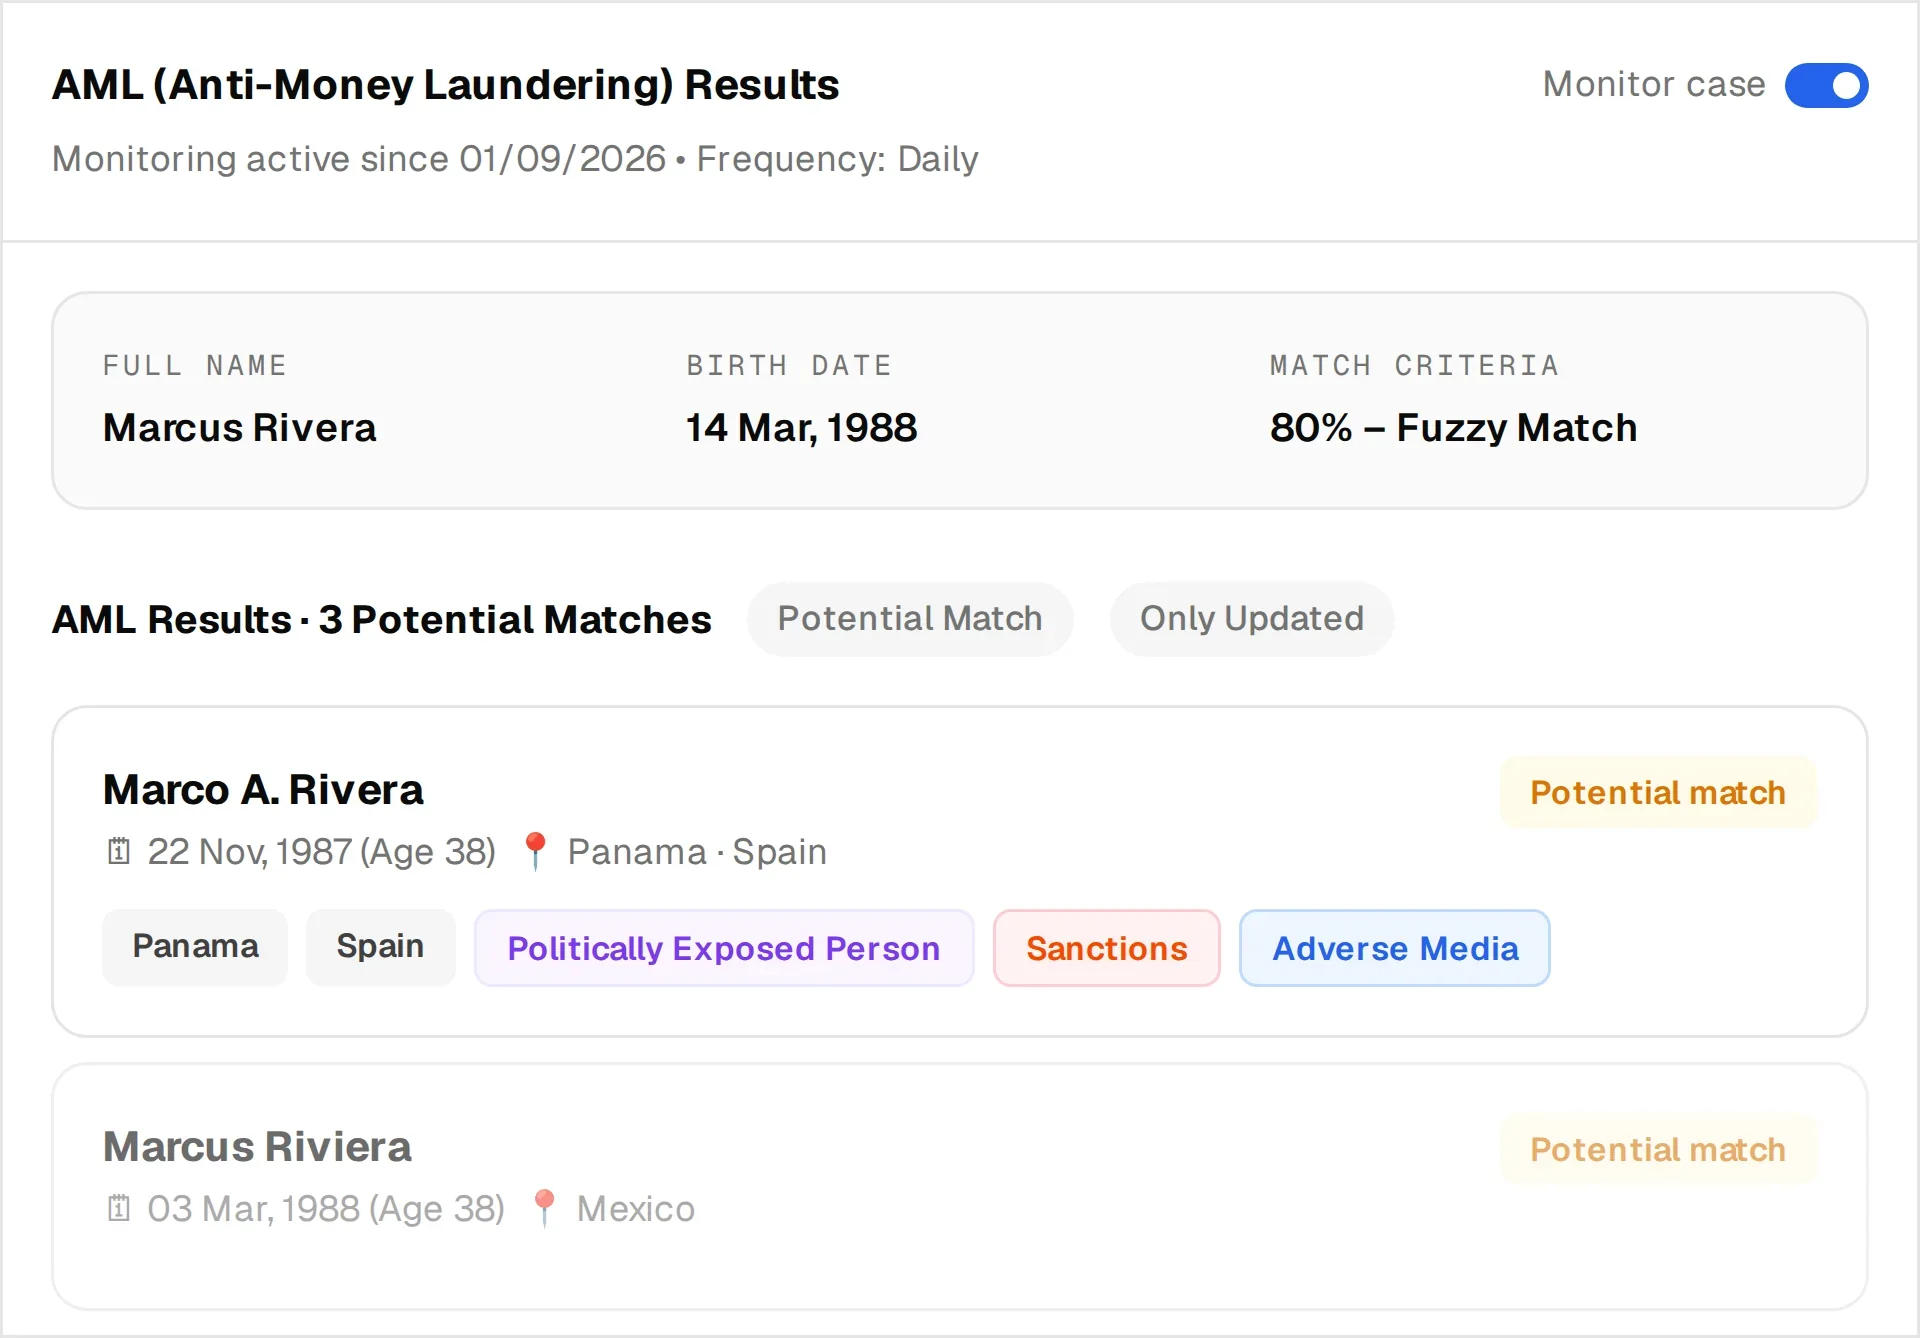
AML screening with continuous monitoring, built for name-match complexity.
Real-time PEP, sanctions, and adverse-media screening tuned for transliteration and regional naming conventions. Every screening action and decision is recorded in a complete audit history for compliance review.
- ✓Fuzzy name matching with configurable % threshold
- ✓Ongoing daily monitoring, new matches fire webhooks
- ✓Full AML audit log per journey, every amendment recorded
- ✓Amend search parameters without re-running the full journey
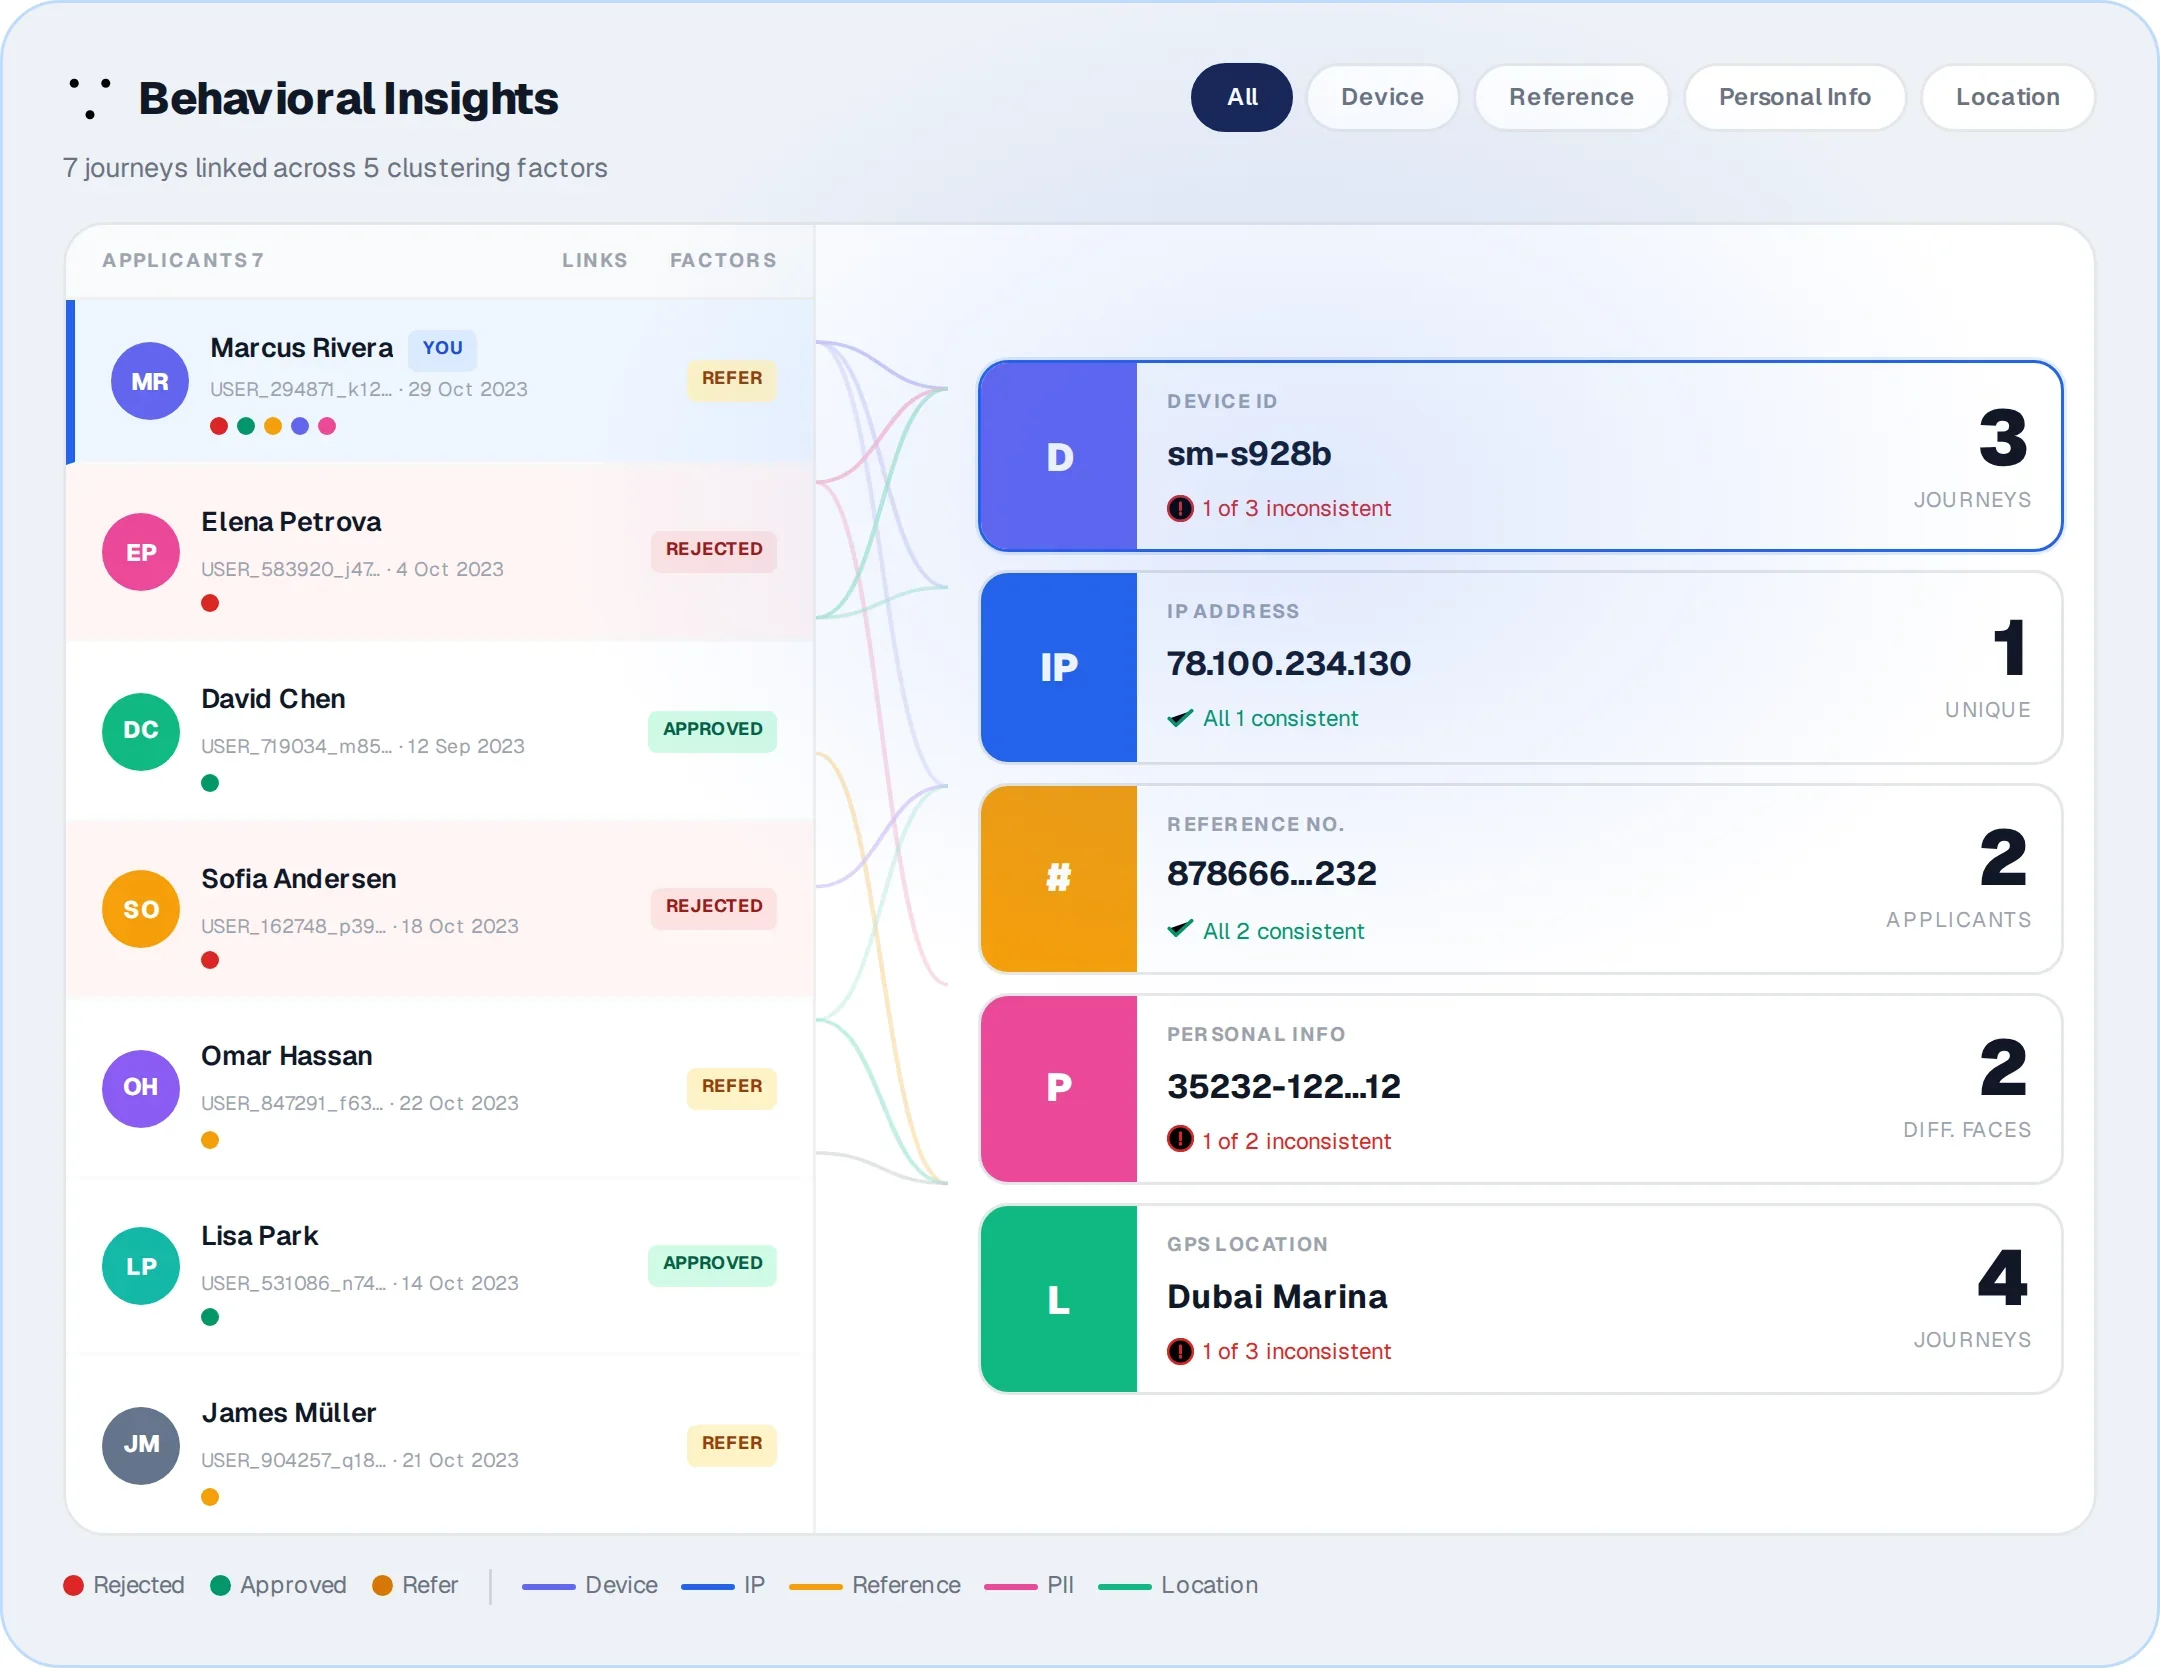
Behavioural detection for the fraud documents can't show.
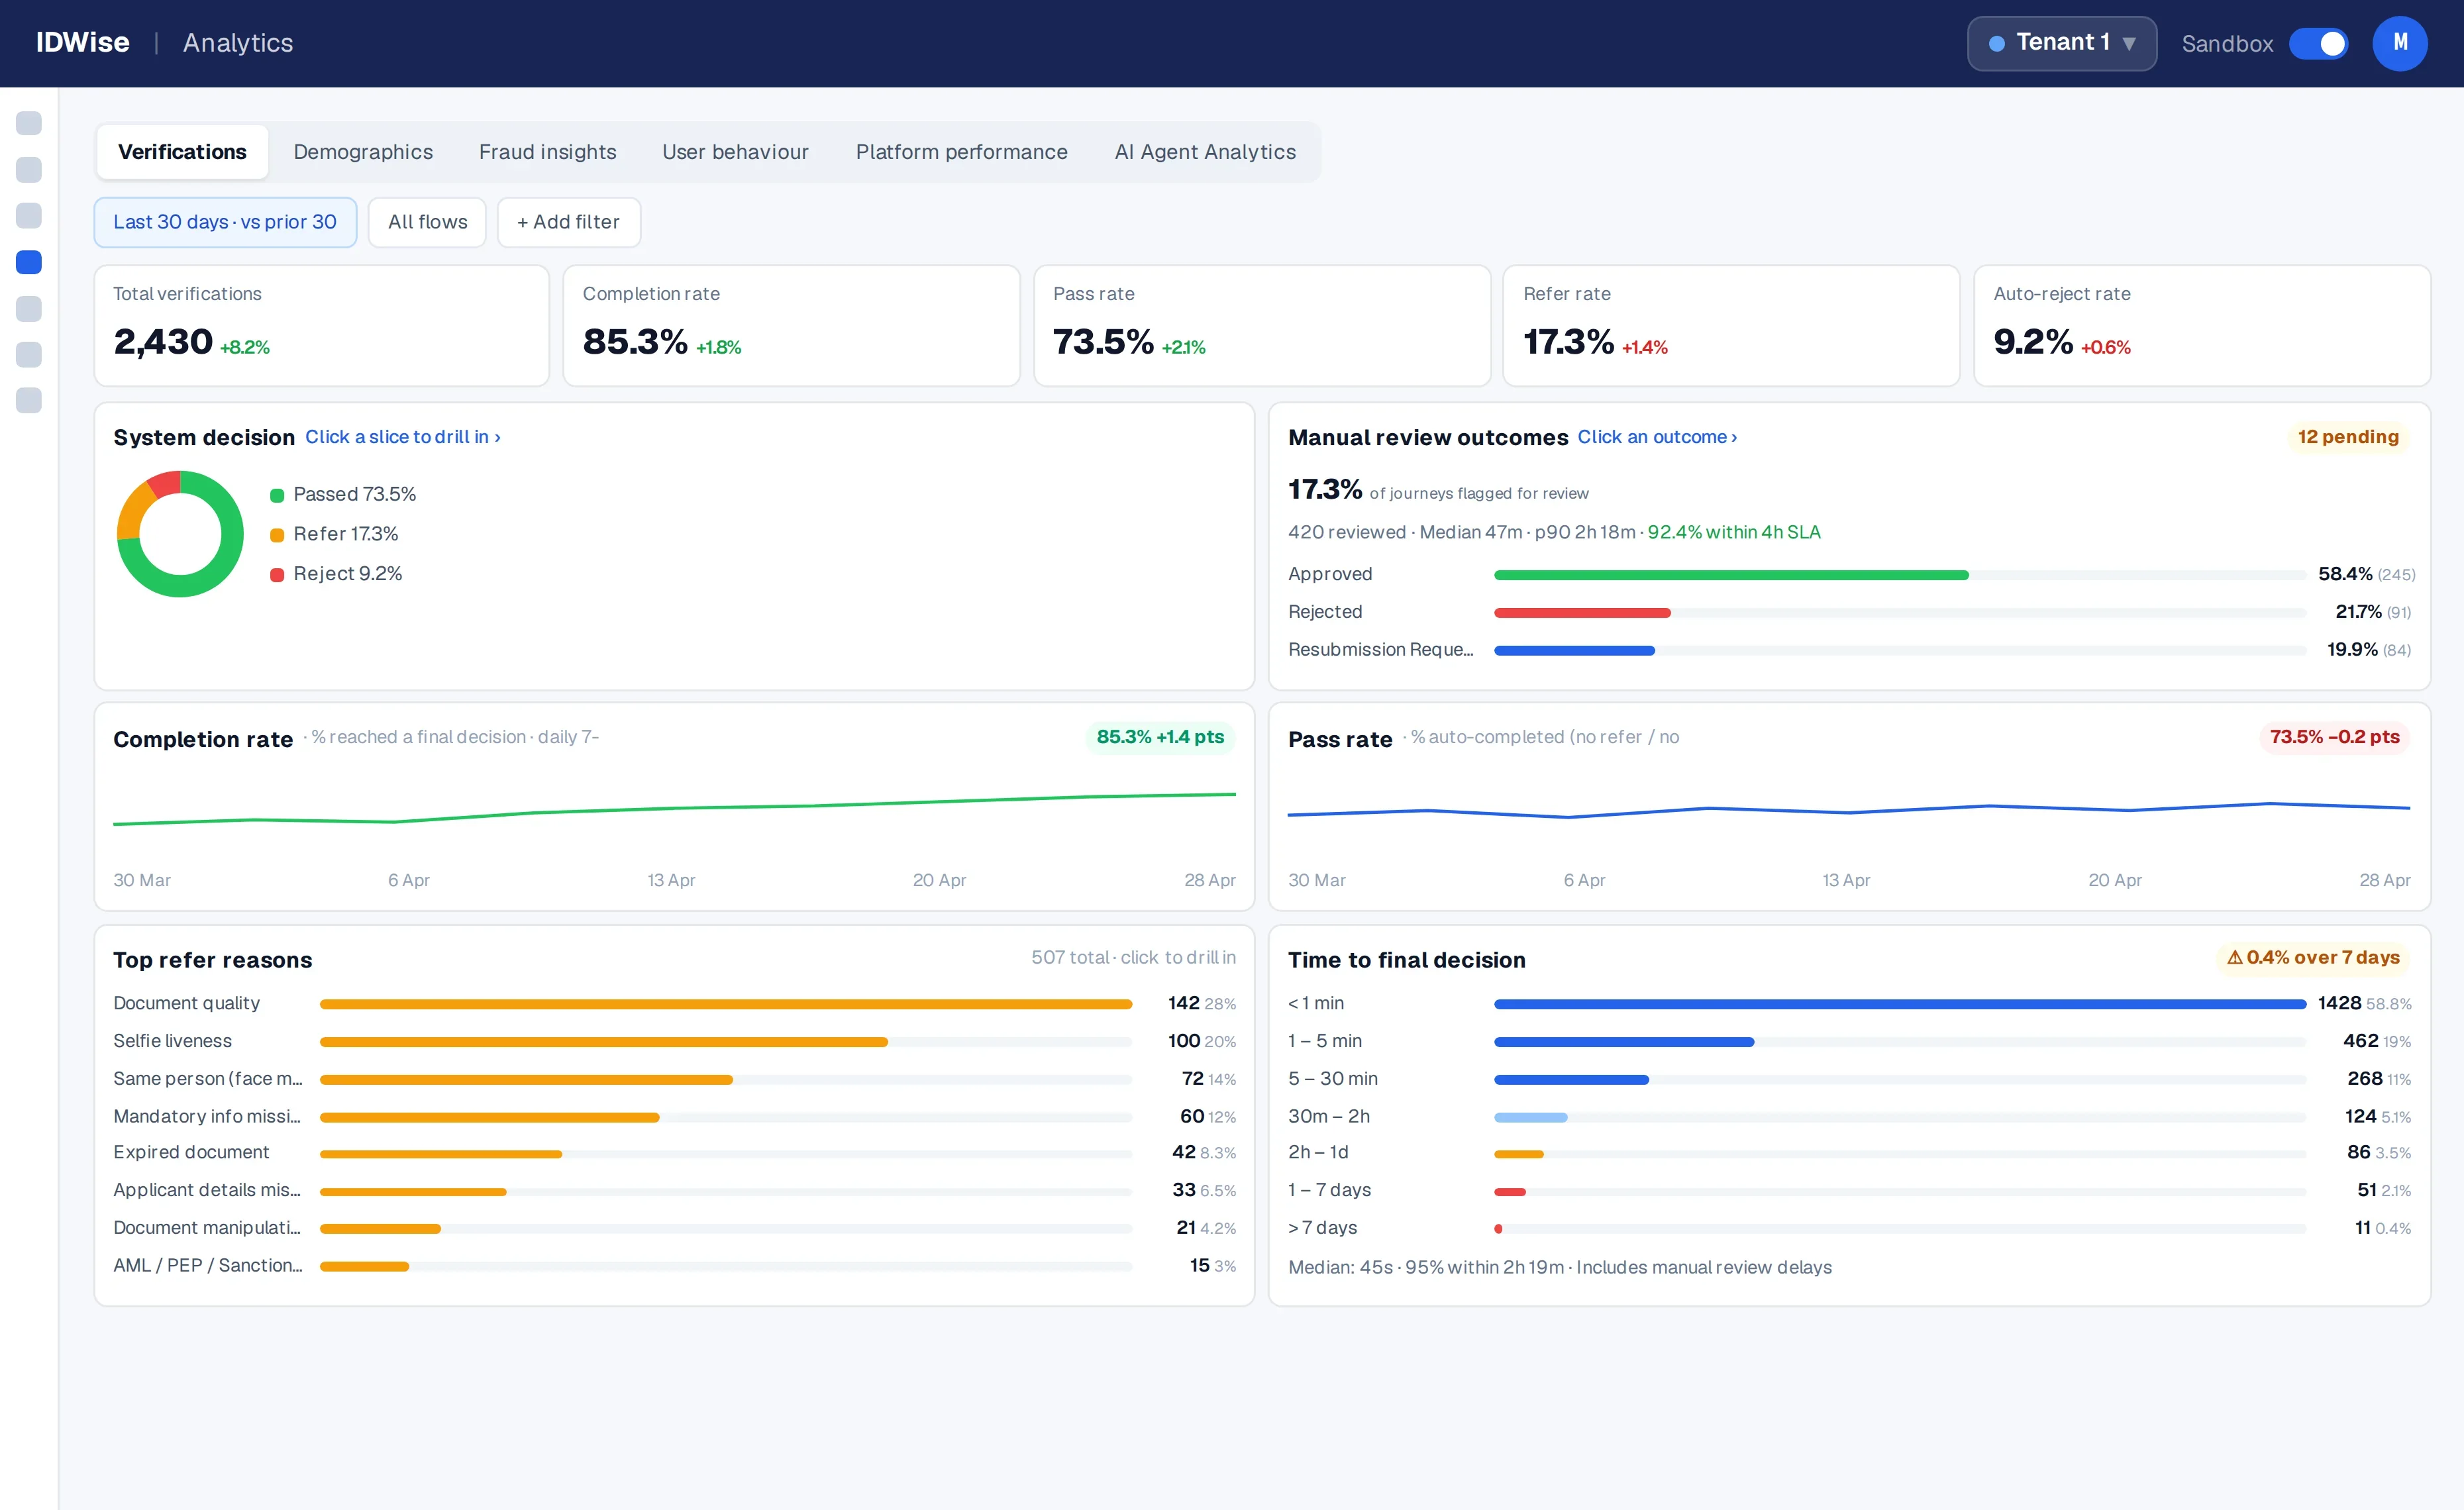
Analyzes user interactions in real time, surfacing organized rings, synthetic identities, and repeat offenders through a bipartite graph that links journeys across device, PII, location, and biometric clustering factors.
- ✓Detect organized attacks & fraud rings
- ✓Catch identity theft & deepfake reuse
- ✓Spot suspicious timing & submission patterns
- ✓Export investigation report with one click
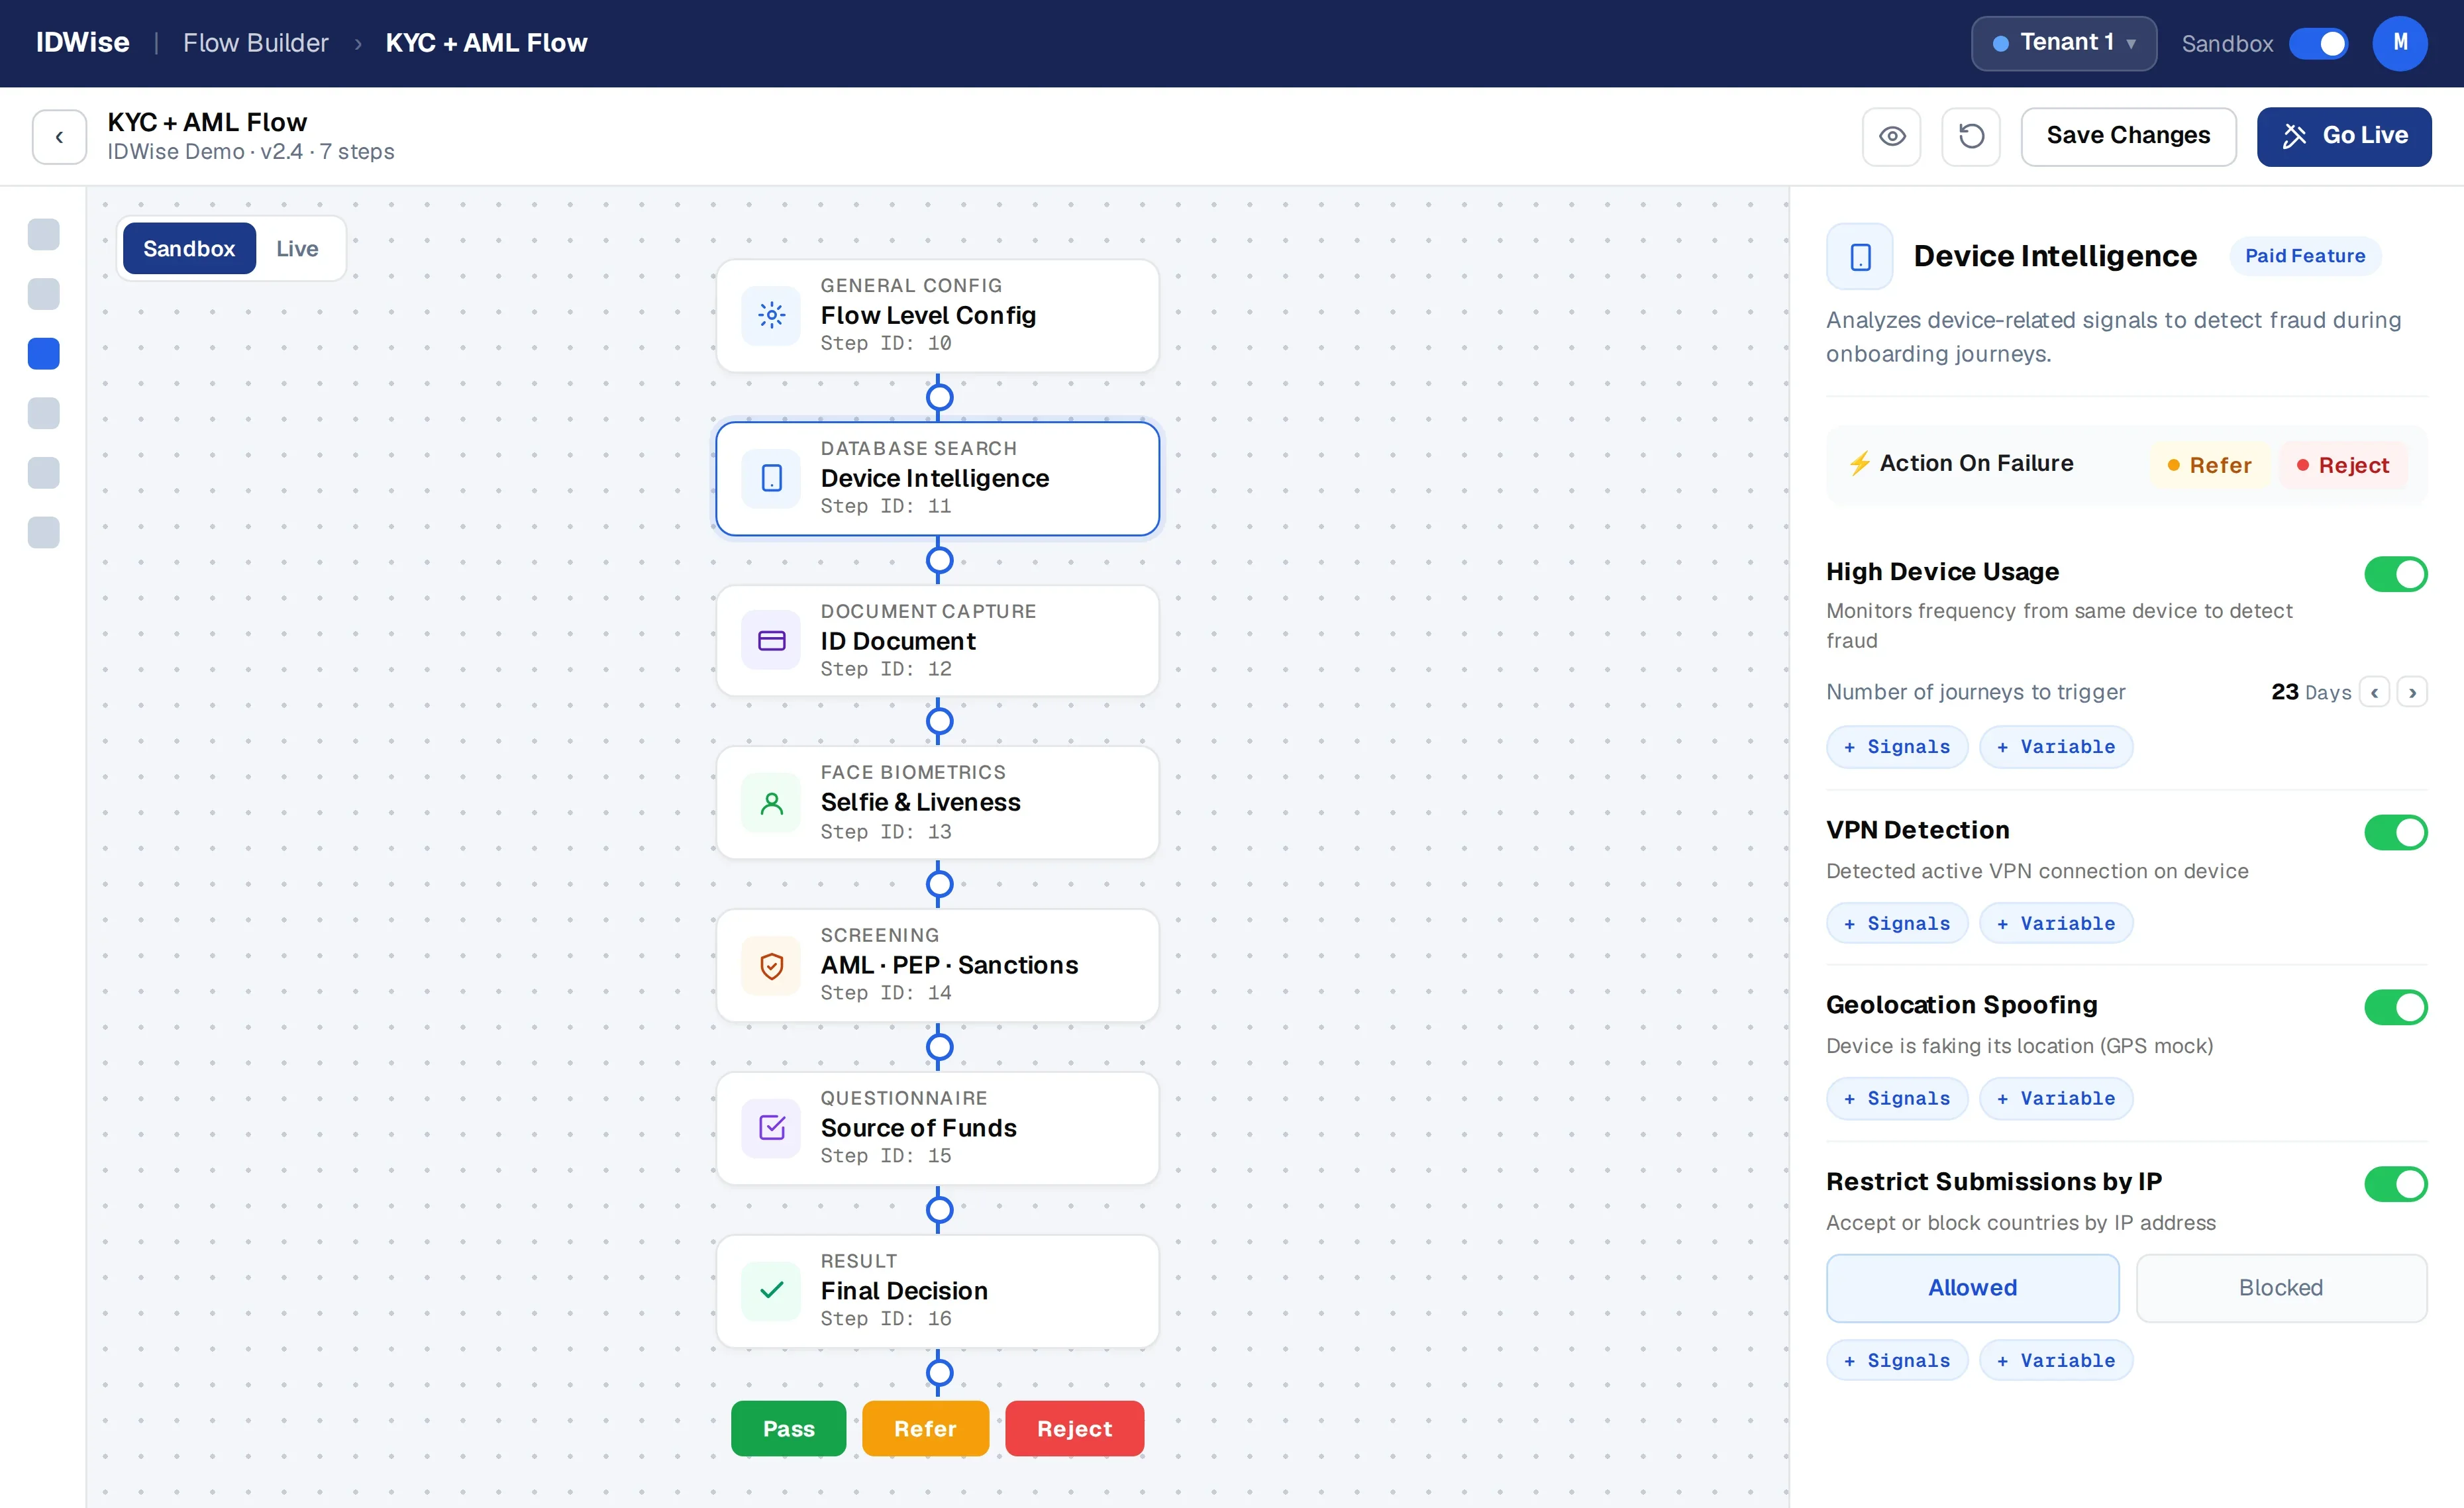
Device intelligence: 20+ signals beneath every journey.
Enhances security by detecting suspicious device activity during onboarding. Apply configurable actions when elevated device-risk signals are detected.
- ✓Flag devices reused across multiple accounts
- ✓Identify VPN, incognito & anti-fingerprinting
- ✓Spot bots, emulators & virtual machines
- ✓Apply configurable actions when elevated device-risk signals are detected
Built for Enterprise Integration.
Get started with a few lines of code. Sandbox from day one, webhooks for every event, and docs your engineers will actually use.
Journey config lives outside the binary, ship policy changes without app-store re-submission or an engineering sprint.
Consistent trust controls and journey configuration across supported channels.
// 1, start a verification journey
const journey = await idwise.startJourney({
  flowId: 'onboarding_uae_retail',
  referenceNo: 'USR_000001',
  locale: 'ar'
});

// 2, receive the decision via API
app.get('journey/v2/get/12345667899', (req) => {
  const { decision } = req.body;
  // Passed | Refer | Rejected
  if (decision === 'Passed') {
    activateAccount(req.body.journeyId);
  }
});
Architecture Designed for Regulated Enterprises.
Built to clear enterprise security reviews, data-protection assessments, architecture committees, and regional residency requirements, without forcing you to assemble or maintain the trust layer yourself.
Regional & private deployment
Deploy on AWS, GCP or Azure, in the data-residency zone your auditor requires. Architecture aligned to regional regulator frameworks.
Hybrid processing model
Verification processing runs on the IDWise platform while the resulting data and evidence are persisted in your own on-premises storage, giving you full control over retention, access and residency without operating the verification stack yourself.
Omni-channel support
iOS, Android, Web, React Native, Flutter and REST API, the same journey configuration, fraud checks and document coverage available across supported channels.
True multi-tenancy
Flows, configs, themes, access rights, audit trails, and residency, isolated per tenant. Maintain isolated configurations by tenant, region and product line.
Configurable retention
Supports configurable retention, scoped storage and data minimisation.
Multi-language, multi-script
RTL scripts, non-Latin character sets, regional conventions. OCR, AML name matching, and capture UX engineered for market specificity.
Enterprise implementation & escalation
Dedicated implementation support and escalation paths available for enterprise deployments.
The hardest part of identity verification isn't the verification. It's the trust infrastructure beneath it, configurable deployment and residency options, consistent trust controls across supported channels, and configurable retention that supports data minimisation.
Procurement-ready for regulated enterprises.
The certifications, contracts, security artifacts, and residency model your CISO, DPO, and external auditors expect, engineered in, not retrofitted. The compliance pack walks in with the demo, not after.
IDWise, explained.
Talk to an IDWise Specialist.
Map your markets, identity requirements, regulatory environment and fraud profile with our team, and see how IDWise fits your operating model.
- ✓A working session, not a vendor pitch
- ✓Live demo on your documents & geographies
- ✓Security & compliance pack on request
- ✓Named implementation support & direct engineering access